Happy Sunshine Corporation
Enterprise Network, Virtualization and Hybrid Infrastructure
New Brunswick Community College · Moncton, Canada
Project overview
A team-based Applied Studies II project for a fictional multi-department company, combining physical Cisco networking, Windows Server and Hyper-V, centralized identity and file services, Linux clients, and AWS-hosted services. The simulated organization was to be represented using physical lab equipment and virtual machines; this was broader than a Packet Tracer-only exercise.
Team context and individual contribution
Joshua Abia is listed as a team member in the original brief; another member held team-lead duties. The brief defines requirements, not completed individual accomplishments. Recovered dated logs now support the individual tasks summarized below.
Technical problem
Provide departmental connectivity and shared resources while limiting broadcast domains and preventing unintended cross-department file access.
Original assignment topology
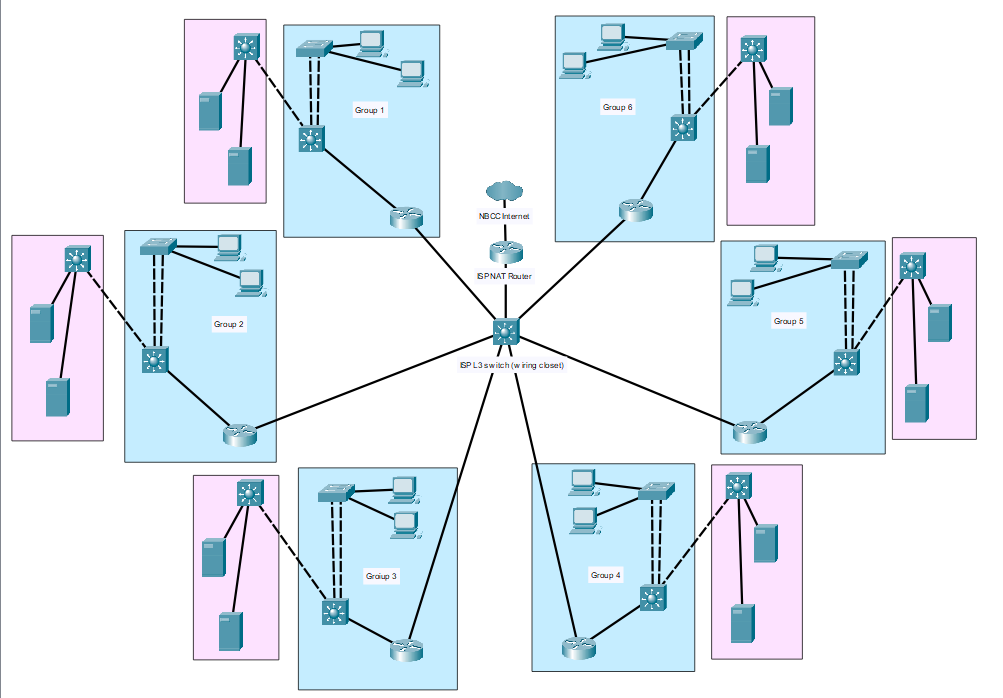
Architecture and objectives
Conceptual illustration of the documented scope, not a recovered topology or proof of connectivity.
- Plan physical, logical and Active Directory architectures using 172.31.112.0/21 and VLSM.
- Derive VLANs and VLSM allocations from department counts, allow for projected 50% staffing growth and keep broadcast domains below 100 hosts. Earlier design notes proposed 11 VLANs; the final allocation spreadsheet has not been verified.
- Include Layer 2/3 switching, 802.1Q trunks, EtherChannel and switch security.
- Document DC1/DC2, the Staff S: drive, group-based NTFS permissions and departmental Documents folder redirection.
Environment and configuration
| Area | Documented scope |
|---|---|
| Addressing | 172.31.112.0/21; VLSM allocation design |
| Segmentation | Department-based VLAN design; fewer than 100 clients per broadcast domain; final count unverified |
| Routing | SVIs, RIPv2 and default-route design |
| Identity | Domain controllers, organizational units and security groups |
| File services | Staff share, departmental permissions and redirected Documents |
Configuration reference
Design and diagnostic reference; not a verbatim successful execution log.
Staff share permission design
IT group: Full Control
Administration group: Modify
Department groups: Modify on their own folders
Ordinary users: Read at the Staff-share root

Folder redirection design
IT / Administration -> DC1 Documents root
Sales / Production -> DC2 Documents root
Create a folder for each user beneath the root
Physical infrastructure and Hyper-V
Requirements documented in the original team-project brief; completion is not implied.
- The brief specifies two rack-mount servers, four Windows/Linux client workstations, a Cisco router, a Layer 2 switch and a Layer 3 switch.
- Install Windows Server and Hyper-V on both hosts and create two domain-controller VMs in the same domain, with LAN-connected and isolated virtual-network options.
- Require remote host administration by designated IT/admin groups, opposite-host VM backups and automatic domain-controller VM startup.
- Demonstrate moving a running VM between hosts with instructor sign-off. The requirement is documented; a sign-off or successful migration result has not been recovered.
Routing, switching and addressing
Requirements documented in the original team-project brief; completion is not implied.
- Use the assigned 172.31.112.0/21 internal range, a point-to-point subnet between office switching and the edge router, and a /30 ISP handoff.
- Provide inter-VLAN routing on the Layer 3 switch, RIPv2 within the corporate network and a default route toward the ISP. Prevent RIP advertisements from leaking onto the ISP-facing connection.
- Build a required 2 Gb aggregate EtherChannel trunk carrying VLAN traffic. This is an assignment target, not a measured throughput result.
- Document port-security and VLAN/STP attack mitigations, save device configurations, then re-test connectivity after hardening.
Windows DHCP and resilient DNS
Requirements documented in the original team-project brief; completion is not implied.
- Configure DHCP options for DNS and default gateways; exclude static infrastructure addresses and the first ten addresses of each subnet.
- Use the specified two-hour lease policy, DHCP reservations for IT clients and backup DHCP service for every scope. Restrict allocation to configured clients and test unknown-client rejection.
- Provide descriptive hostnames, A/NS records, fault-tolerant DNS and cross-team FQDN resolution. Meet the specified two-hour zone-transfer requirement for zones not integrated with Active Directory.
Windows identity, delegated administration and file services
Requirements documented in the original team-project brief; completion is not implied.
- Create departmental OUs and groups; map employee home folders to H: and the central Staff share to S:.
- The brief places the Staff share on a non-domain-controller VM, while a later annotated UNC example conflicts with that placement. Verify the final storage host before claiming implementation.
- Use group-based NTFS access: read-only Staff root for ordinary users, Full Control for IT and Modify for Administration, with department-restricted subfolders.
- Create Documents shares on both domain controllers and configure departmental Group Policy folder redirection.
- Implement the specified differentiated password policies, delegated user/password administration, login notice, command-prompt restriction with administrator exceptions and policy-inheritance rules.
- Use remote administration tools from Windows clients rather than requiring RDP into every server.
AWS hosting, domain delegation and backup
Requirements documented in the original team-project brief; completion is not implied.
- Register a project domain and delegate its DNS hosting to Route 53 through registrar nameserver changes. DNS delegation is distinct from transferring domain registration.
- Host a corporate website on a Windows EC2 instance and a separate static bulletin-board proof of concept in S3.
- Plan a proof-of-concept pair of cloud domain controllers in a private subnet, with replication and cost documentation as validation targets.
- Plan documentation tier transitions at 30 and 90 days. Standard S3 Lifecycle transitions are age-based; the brief’s “not accessed” wording requires an explicit design interpretation, not an unsupported inactivity claim.
- Apply public-access, cost-centre, creator and last-change tags and manage the limited learner-lab credit budget.
- Schedule daily 6:00 AM rsync backups from a mounted Windows Staff share through a Linux client to an EC2 Linux instance. Retained execution and restore-test results are not established by the brief.
Linux integration and remote administration
Requirements documented in the original team-project brief; completion is not implied.
- Use two Linux distributions for IT/Production workstations, with static and DHCP addressing, DNS registration, sudo-enabled lab accounts and a consistent technical toolset.
- Script mount-point creation and Windows Staff/Documents share mounting, with the specified login-triggered execution.
- Configure OpenSSH with differentiated key-only and key-or-password authentication for designated accounts.
- Treat the brief’s root-SSH and legacy Telnet allowances as historical lab requirements, not production security recommendations.
Engineering delivery and validation
Requirements documented in the original team-project brief; completion is not implied.
- Prepare physical, virtualization and Active Directory diagrams, an addressing plan, role inventory, responsibility matrix and deployment sequence.
- Obtain instructor plan approval before physical implementation, maintain meeting minutes, and use Spiceworks tickets for major tasks and unexpected issues.
- Maintain dated individual activity logs identifying completed tasks, collaborators, problems and outcomes.
- Validate VLAN/routing reachability, DHCP failover, DNS resolution, NTFS permissions, policy results, VM backup/migration and cloud connectivity independently.
Troubleshooting
Balance departmental subnet sizes against host-capacity requirements; account for physical port availability when planning EtherChannel. Separate share access from NTFS authorization and allow Group Policy to create per-user folders beneath the redirection root.
Security considerations
Use security-group membership for authorization rather than individual-user ACLs. Validate both permitted departmental access and denied cross-department access.
Evidence and verified outcomes
The newly supplied original Applied Studies II brief confirms the team context, equipment list, network range, Windows/Linux integration, AWS requirements and documentation workflow. Its three embedded images are a decorative graphic, the classroom topology reference and a domain-provider offer; they do not prove deployment. A related PowerShell script independently demonstrates CSV-to-Active Directory provisioning logic, but does not establish successful execution. Recovered logs now document individual tasks and reported permission/policy tests; final network acceptance and instructor sign-offs remain unverified.
Historical academic work. No current cloud service, production deployment, performance metric or certification is implied.
Skills demonstrated in the documented scope
Source and validation notes
Expanded from the owner-provided Applied Studies II project brief and earlier NBCC technical history. Teammate names, instructor contact details, credential-like annotations and raw configuration paths are excluded. The original DOCX is retained locally rather than offered as a public download.
View additional technical labs →Recovered implementation and individual contribution
Dated logs now record Joshua’s AD design, router configuration, Windows 10/RSAT setup, OU/user creation, H: home-drive work and permission/GPO tests. February 19 records correcting Staff/Documents placement and rebuilding permissions. These are recorded academic contributions, not independent instructor sign-off.
The actual router command export contains interface addressing, a default route and RIPv2. Eleven VLANs remain a recovered design target; a final complete VLAN/subnet worksheet was not found. Packet Tracer exercises and the physical-equipment project are distinct.
! Selected actual router-command excerpt; credentials omitted
router rip
 version 2
 passive-interface g0/0/1
 default-information originate
Recovered commands are not successful route output. Final all-VLAN reachability, DHCP failover, EtherChannel throughput and instructor sign-offs remain unverified.