pfSense to Azure
Hybrid Site-to-Site VPN
New Brunswick Community College · Moncton, Canada
Project overview
Configure and diagnose an IPsec site-to-site connection between a simulated on-premises environment and an Azure virtual network.
Technical problem
Establish a secure routed connection between local systems and cloud-hosted workloads, then diagnose negotiation and reachability failures.
Architecture and objectives
Conceptual illustration of the documented scope, not a recovered topology or proof of connectivity.
- Define the local 172.16.1.0/24 network, Azure 10.1.0.0/16 VNet and 10.1.1.0/24 gateway subnet.
- Work with Azure Virtual Network Gateway and Local Network Gateway definitions.
- Configure pfSense Phase 1/Phase 2, pre-shared-key authentication and encryption/integrity/key-exchange settings.
- Investigate authentication errors, routing, subnet selectors and firewall rules.
Environment and configuration
| Area | Documented scope |
|---|---|
| Local network | 172.16.1.0/24 |
| Azure network | 10.1.0.0/16; gateway subnet 10.1.1.0/24 |
| Target negotiation | IPsec / IKEv2 with pre-shared authentication |
| Cryptography scope | AES-256, SHA-256 and Diffie-Hellman compatibility |
| Historical result | AUTHENTICATION_FAILED; zero active connections reported |
Configuration reference
Design and diagnostic reference; not a verbatim successful execution log.
Diagnostic checklist
1. Compare peer authentication and shared-key configuration
2. Compare IKE version and Phase 1 proposals
3. Compare Phase 2 selectors and transforms
4. Inspect gateway connection status and negotiation logs
5. Validate routes/firewall rules before testing traffic
Troubleshooting
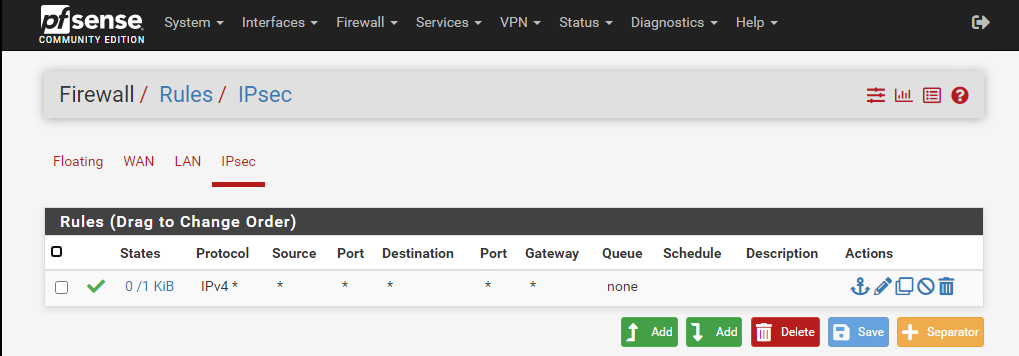
Historical records reported AUTHENTICATION_FAILED and zero active connections. Configuration screenshots demonstrate work on the tunnel and firewall rule, but do not prove that the endpoints negotiated successfully. An inspected legacy screenshot showed Auto/main negotiation, so IKEv2 should be read as target scope rather than a verified final setting.
Security considerations
Never publish the pre-shared key. A permissive historical lab firewall rule is configuration evidence, not a recommended production policy.
Evidence and verified outcomes
Applied pfSense Phase 1/Phase 2 configuration and an IPsec firewall rule were seen in original screenshots. Successful tunnel establishment, bidirectional ping and private RDP were not confirmed. The VPN remains a troubleshooting case study.
Historical academic work. No current cloud service, production deployment, performance metric or certification is implied.
Skills demonstrated in the documented scope
Screenshot evidence
Source and validation notes
Based on the owner-supplied NBCC technical portfolio history and the bounded local evidence described above. Raw submissions and configuration exports are withheld from public download pending review for credentials, personal information and publication suitability.
View additional technical labs →Lab architecture reference
