Microsoft Azure
Secure Cloud Infrastructure Deployment
New Brunswick Community College · Moncton, Canada
Project overview
Provision Windows and Linux IaaS resources and examine how virtual networks, network interfaces, security rules and remote administration fit together.
Technical problem
Build a manageable cloud-server environment with explicit network boundaries and access controls.
Architecture and objectives
Conceptual illustration of the documented scope, not a recovered topology or proof of connectivity.
- Create resource groups and provision Windows Server 2022 Azure Edition and Ubuntu virtual machines.
- Configure VM sizes, disks, NICs, virtual networks, subnets and public-IP dependencies.
- Use Azure PowerShell, including New-AzVm, for provisioning workflows.
- Associate NSGs with interfaces and examine RDP, SSH and web-access rules.
Environment and configuration
| Area | Documented scope |
|---|---|
| Compute | Windows Server 2022 Azure Edition / Ubuntu |
| Network | VNet, subnets, NIC and public-IP resources |
| Access control | NSG inbound rules and NIC associations |
| Administration | Azure Portal, Azure PowerShell, RDP and SSH |
Configuration reference
Design and diagnostic reference; not a verbatim successful execution log.
# Reference workflow; not a retained execution transcript
New-AzResourceGroup -Name lab-rg -Location canadaeast
# Provision VM/network resources with reviewed parameters
Get-AzVM
Get-AzNetworkInterface
Get-AzNetworkSecurityGroup
Troubleshooting
Investigate an existing NSG association on a network interface before trying to re-associate it. Check dependency order, firewall permissions and management ports when a VM is unreachable.
Security considerations
Restrict management traffic to approved sources, review NIC/subnet security rules and avoid exposing unrestricted administrative access.
Evidence and verified outcomes
Reviewed original screenshots confirm a completed historical Ubuntu deployment, NIC private-IP/subnet configuration, and a successful IIS feature installation through Run Command. A separate original screenshot shows the IIS welcome page over HTTP, and another shows ping recovery after initial failure; those images are retained locally because they expose additional identifiers. Earlier evidence also confirms an NSG-to-VM-interface association. These are bounded historical lab results, not a claim of current service availability.
Historical academic work. No current cloud service, production deployment, performance metric or certification is implied.
Skills demonstrated in the documented scope
Screenshot evidence
Original academic lab screenshots. Captions state the visible result and its limits.
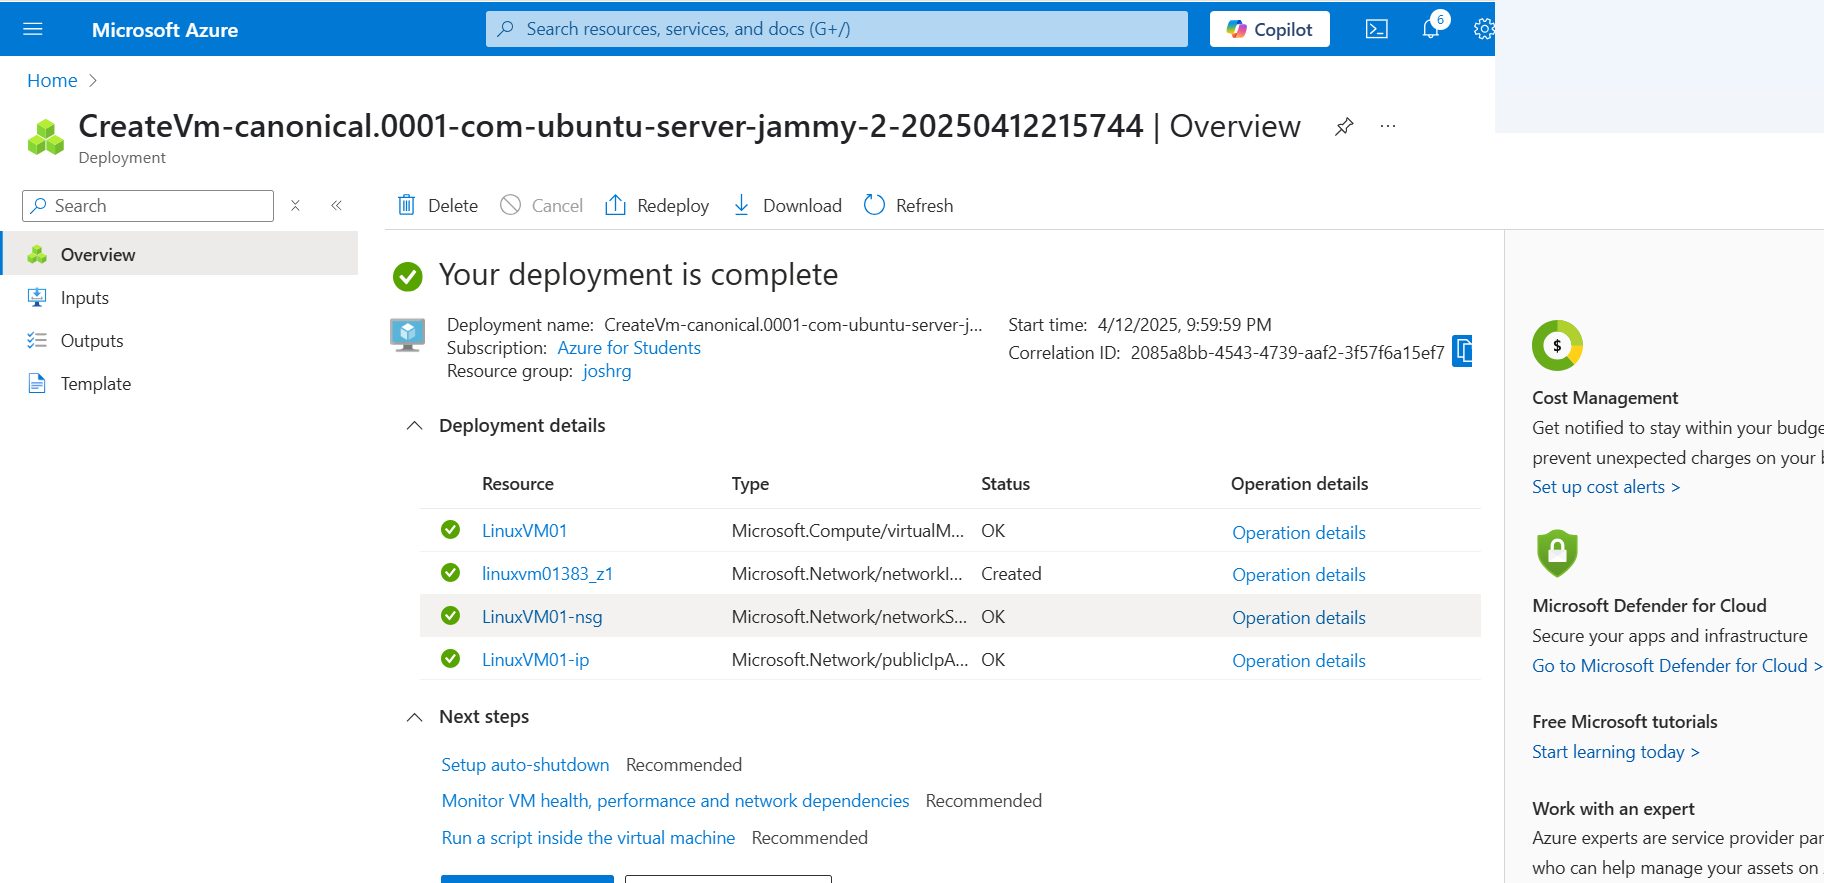
Azure Portal reports a completed historical Ubuntu deployment and successful resource statuses.
Open full size ↗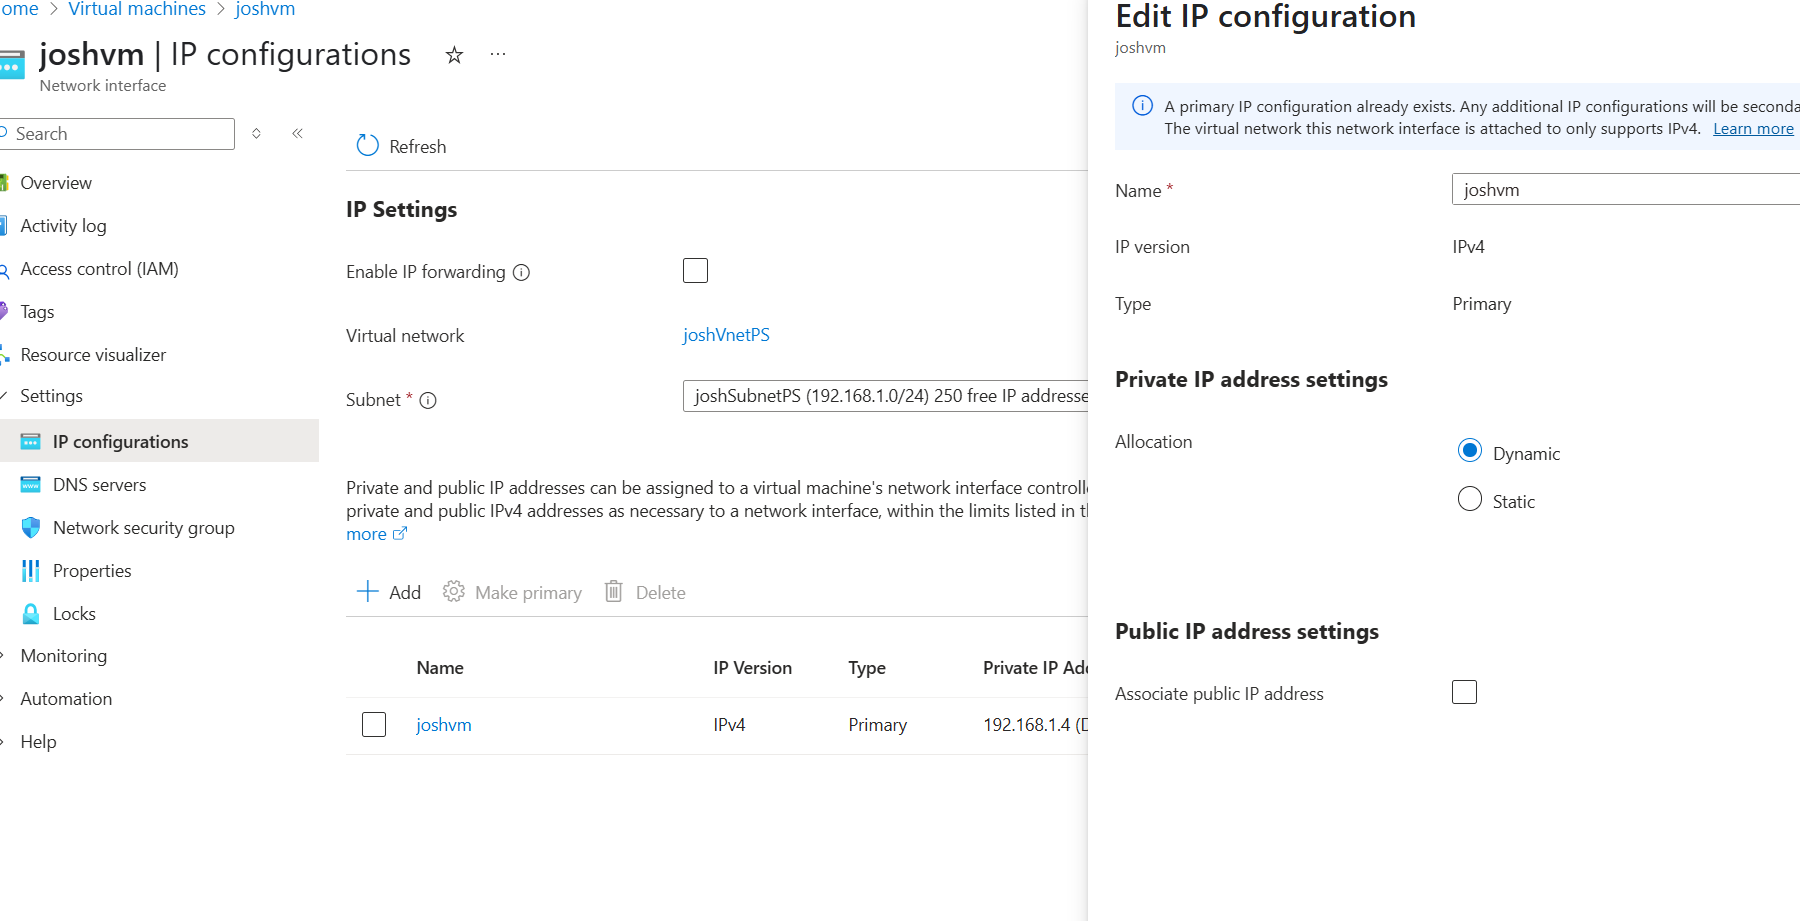
Historical NIC configuration shows its VNet, subnet and dynamic private-IP allocation.
Open full size ↗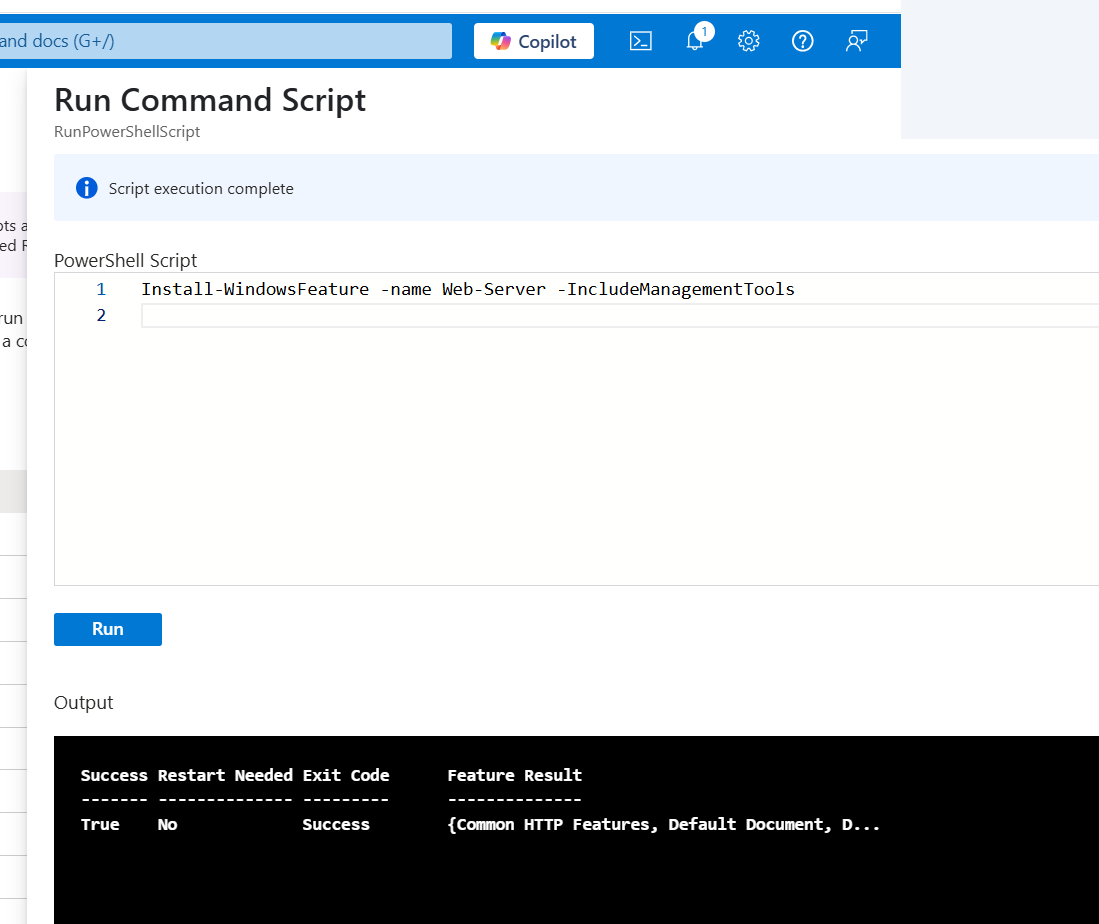
Run Command shows Install-WindowsFeature for Web-Server with Success=True and a successful exit status.
Open full size ↗
Defender displays JIT port and time-range settings. A completed access request is not shown.
Open full size ↗Source and validation notes
Based on the owner-supplied NBCC technical portfolio history and the bounded local evidence described above. Raw submissions and configuration exports are withheld from public download pending review for credentials, personal information and publication suitability.
View additional technical labs →