Azure Policy and Monitoring
Architecture and implementation
Azure resources send telemetry through a Data Collection Rule to Log Analytics. Policy assignments govern deployment choices. Captions distinguish validation, association, query data and alert configuration.
// Illustrative query, not a new execution
Heartbeat
| summarize count() by Computer
Do not infer alert delivery, complete coverage or remediation from saved configuration.
Azure Policy and Monitoring
Objective
Apply governance controls and inspect resource compliance and monitoring.
Technologies
Azure Policy · Resource locks · Log Analytics · Azure Monitor
Configuration summary
Scope includes policy assignments, allowed VM SKUs, remediation concepts, deletion locks, monitoring agents and Data Collection Rules.
Troubleshooting
Separate deployment success from policy compliance and from successful telemetry ingestion.
Evidence and results
Reviewed screenshots show DCR validation passed, VMs listed under the rule, charted Heartbeat-query data, an existing log-search alert rule, and policy assignment review settings. This supports historical monitoring configuration and query activity. Complete coverage, policy remediation and alert delivery are not verified.
Screenshot evidence
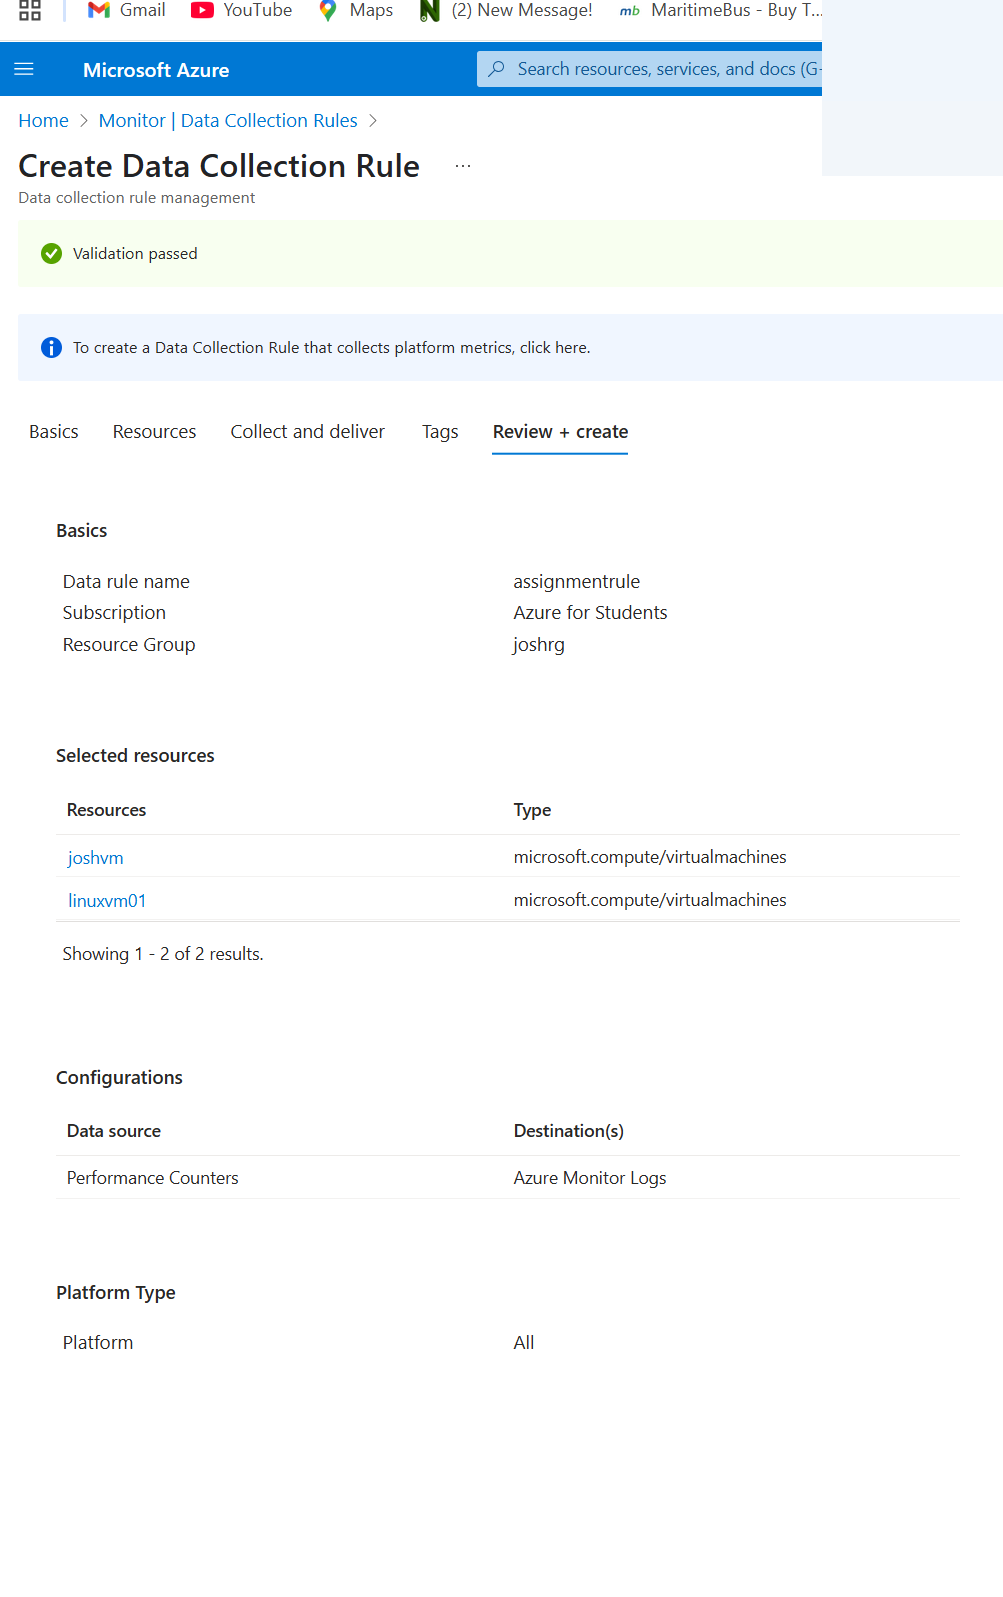
The review screen passed validation. Validation alone is not evidence that telemetry was ingested.
Open full size ↗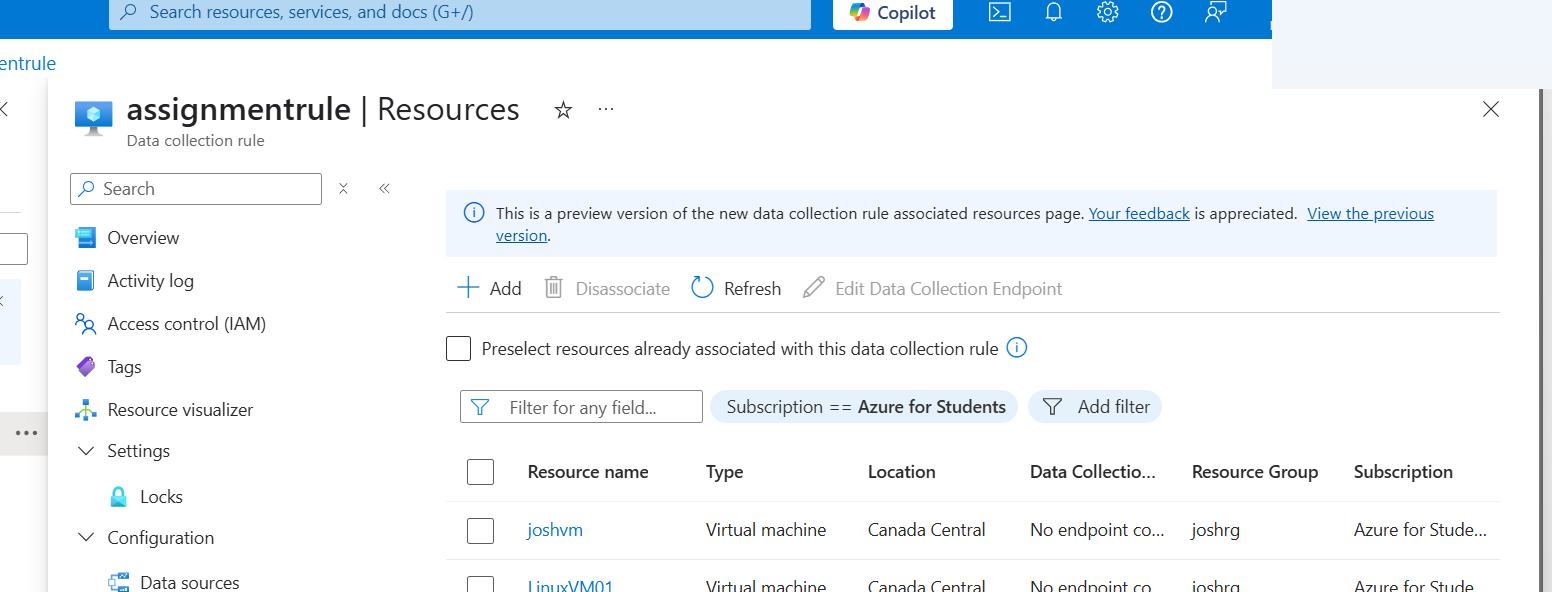
The DCR resource view lists associated VMs. Association does not independently establish agent health.
Open full size ↗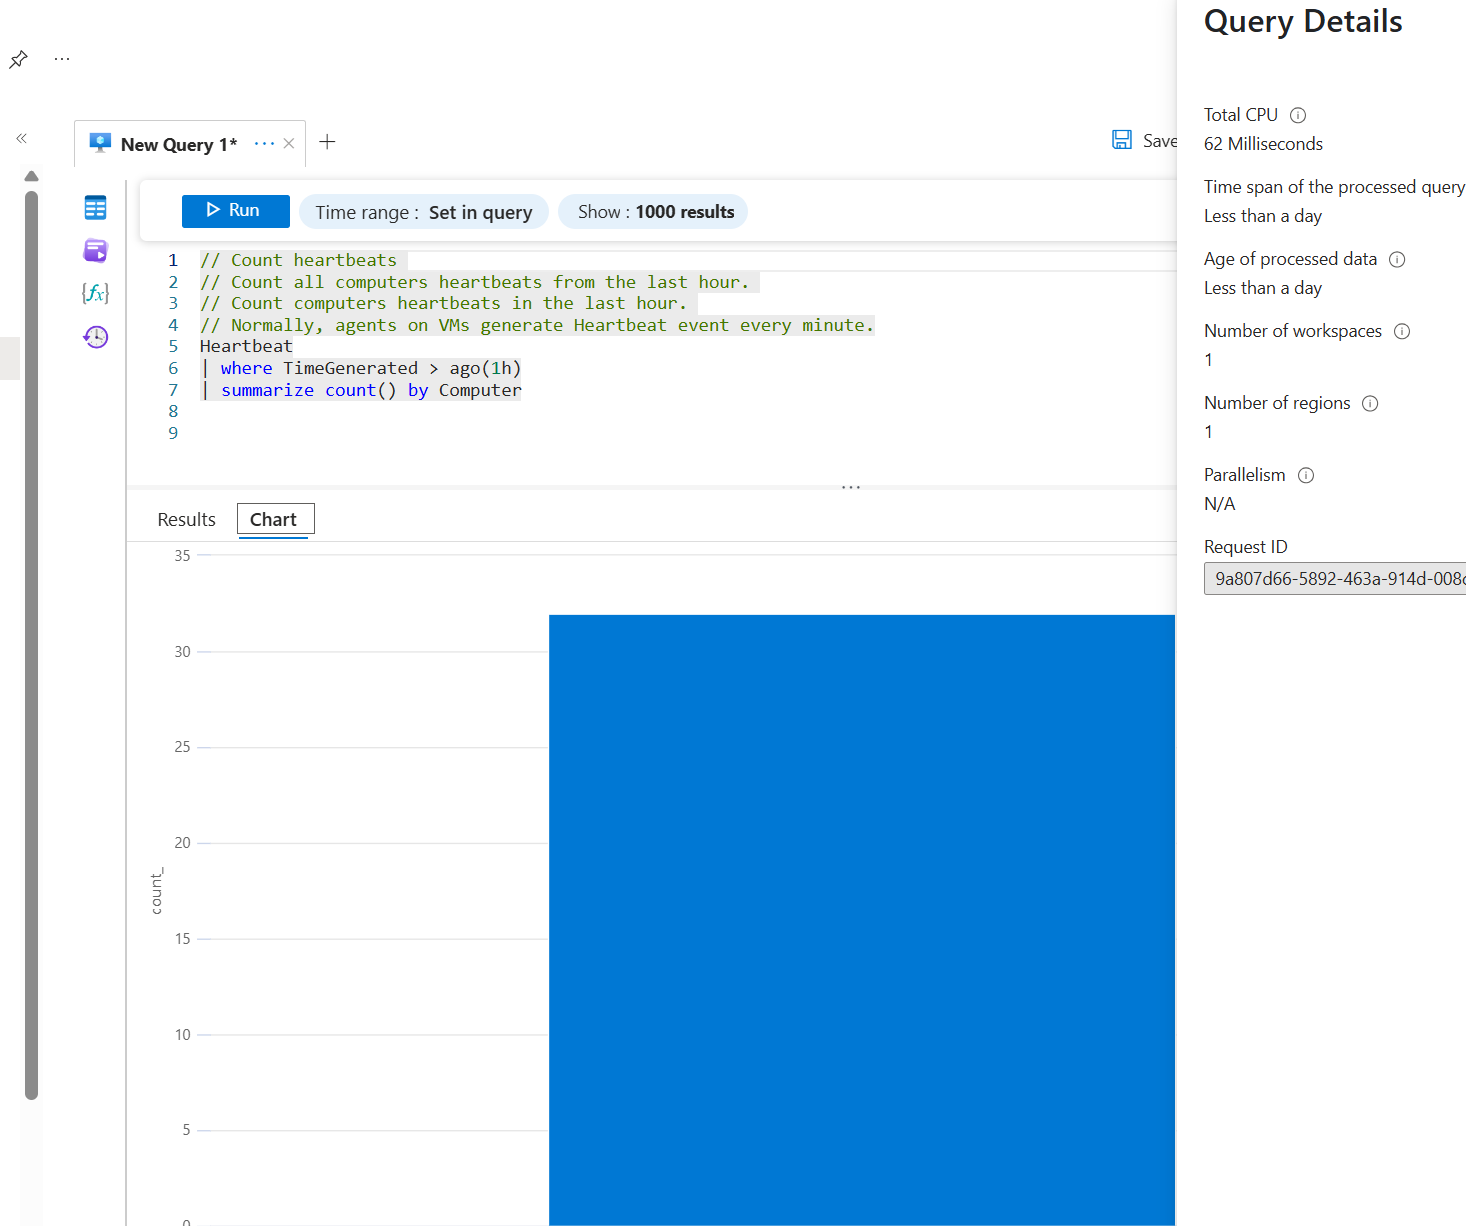
A Heartbeat query and chart demonstrate historical telemetry-query activity, without proving complete monitoring coverage.
Open full size ↗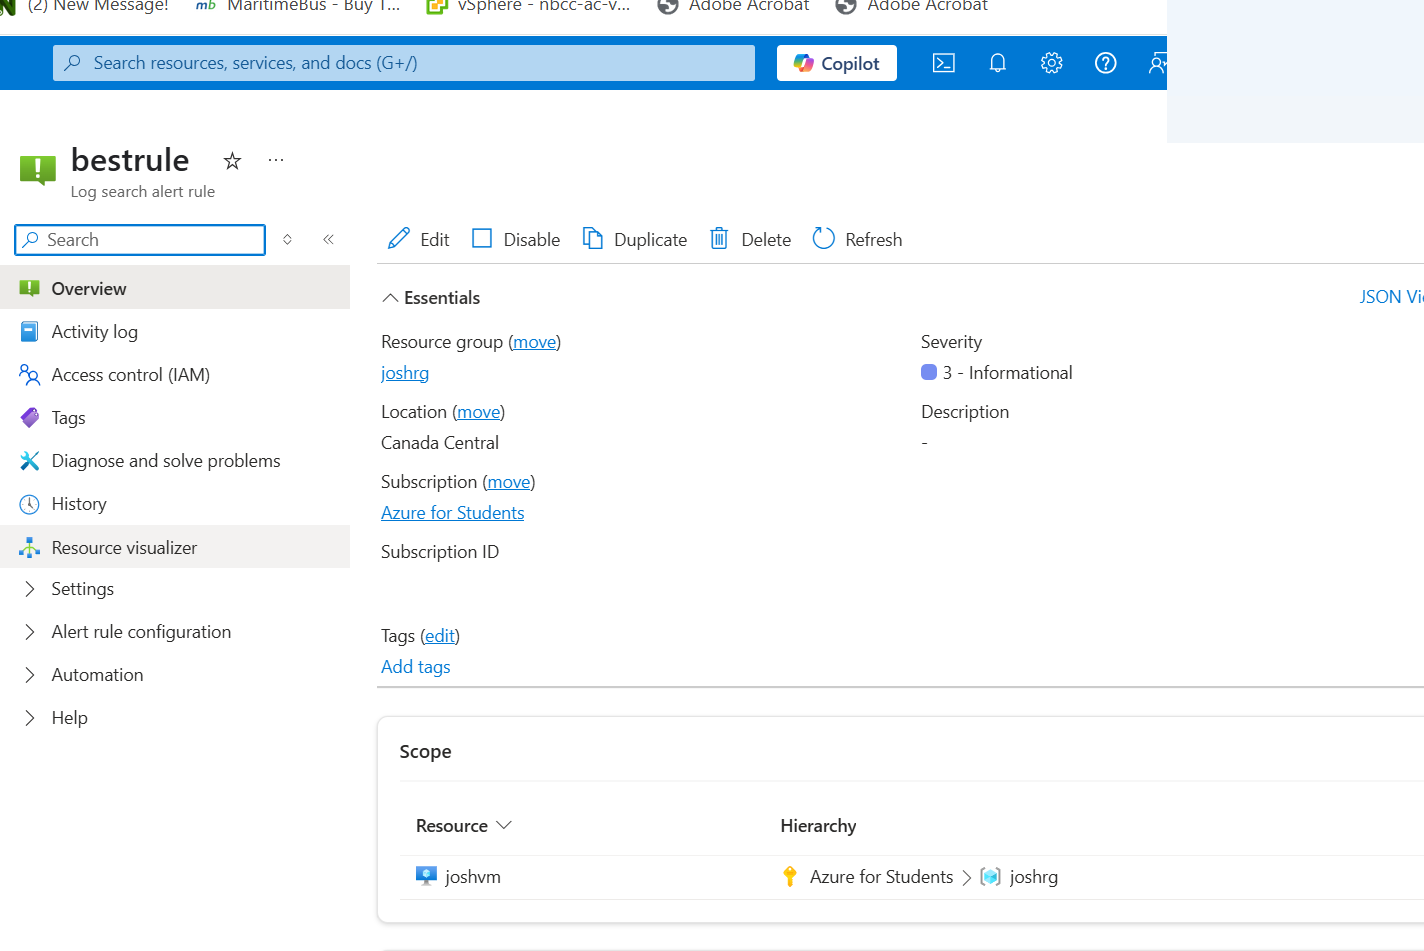
The alert overview shows a saved informational rule. No alert delivery or incident-response test is shown.
Open full size ↗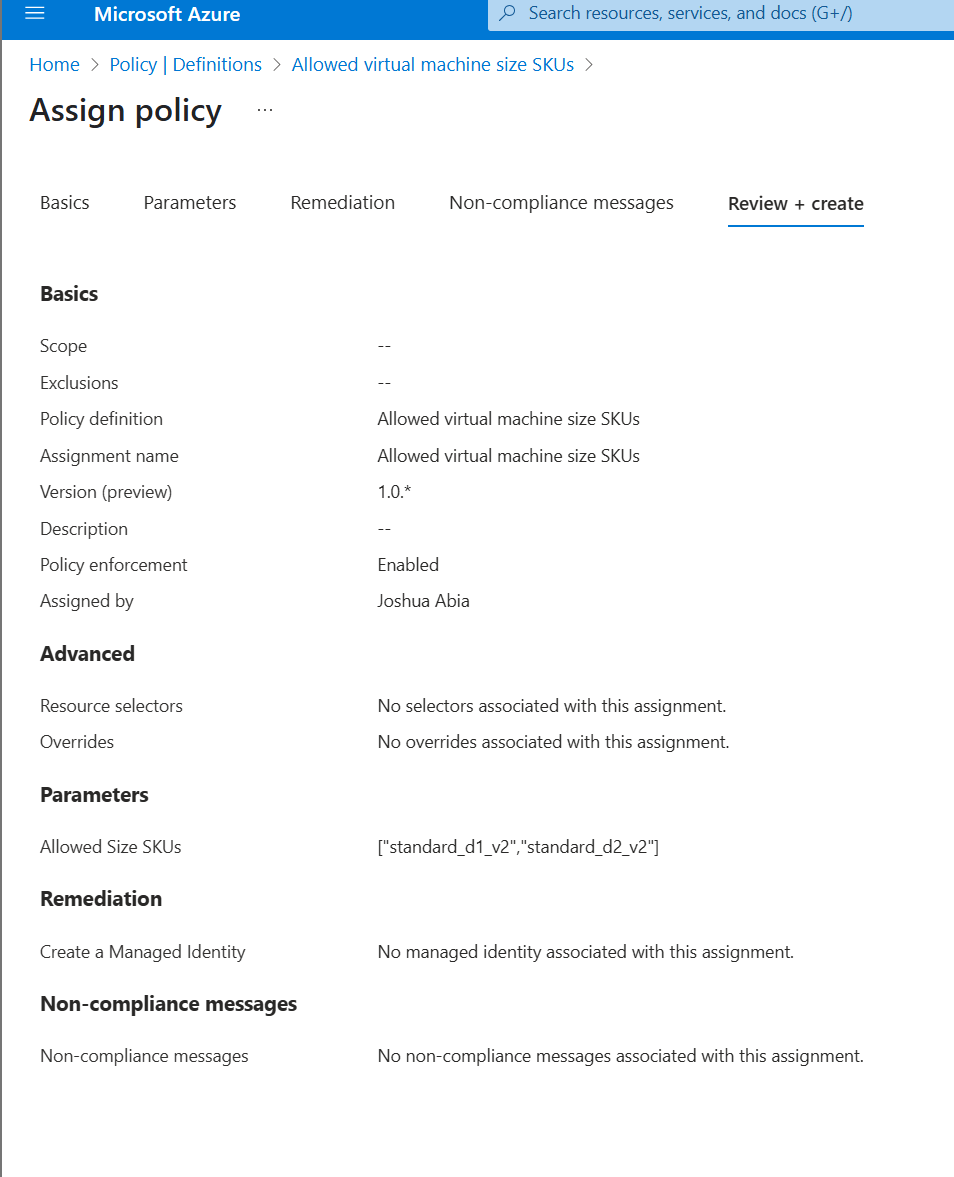
The assignment review lists allowed VM sizes and enforcement settings. This is not a final compliance result.
Open full size ↗